FBI Investigates Hackers' Claim of Stolen Employee Data From Federal Jobs Website
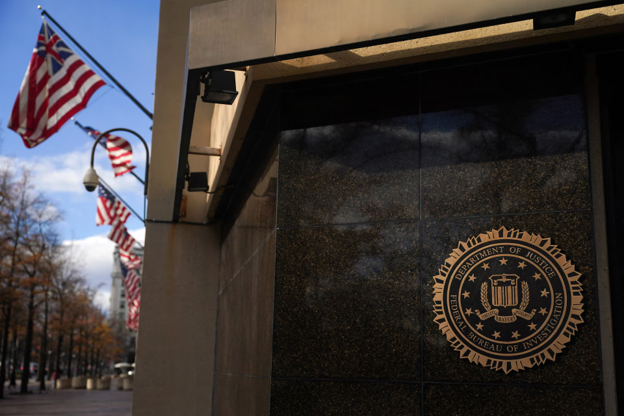
A hacking group over the past week, claimed that it had successfully broken into the bureau’s official job portal and successfully walked away with sensitive personal information about currently enlisted agents as well as other job applicants for the bureau and while the legitimacy of the claim continues to be investigated, the bold claim was enough to suspend the site temporarily until the investigation is complete.
Table of Contents
1. What the Hackers Are Claiming
2. The FBI's Official Response
3. Who Is ShinyHunters
4. Timeline of Events
5. Why This Breach Is Different
6. The FBI's History as a Hacking Target
7. What This Means for Applicants and Employees
8. Conclusion
What the Hackers Are Claiming
In a virtual message addressed directly to the FBI Director Kash Patel and the bureau’s assistant director- who’s responsible for the cyber division, the hacking group made direct claims of having compromised the sensitive data that possibly involved every FBI Agent currently employed with the bureau alongwith the data of those individuals who had recently or sometime in the past, applied for a job with the bureau. The hacker group also named themselves as “ShinyHunters” while making the striking claim. FBIJobs.gov, the site in question isn’t simply a simple database or an internal system, but the public-facing portal that allows citizens to view openings and file their own applications and details, and an attack and leak of data could be massive if the claim is to be found true, raising various concerns about the FBI’s own cybersecurity and digital space.
The FBI's Official Response
The FBI was prompt to provide a response. In a statement issued on Wednesday, the FBI acknowledged that it had become aware of a cyber-criminal group claiming to have compromised the FBI’S government job portal with a possible consequential impact on every FBI Employee’s personal identity. While the acknowledgement was limited to the claims, and did not specifically delve into the legitimacy of the claim, it’s important to monitor how the next chapter unfolds in the near future. The bureau during its statement, selectively chose to acknowledge that it works directly with third-party vendors who aid to run and support the job sites, a factor that has given the matter an active and addressive investigation approach instead of the routine pattern of cyber claims prior to confirmation. The FBI Jobs portal was swiftly made offline as the team began its investigation, a sharp statement that the Agency wasn’t going to be taking chances of others exploiting or repeating the claimed attack before it can be fixed.
Who Is ShinyHunters
ShinyHunters have over the years built a reputation as one of the most prolific data-extortion operations groups with a record of typically targeting companies and organizations by following a standard process of stealing large data sets and then selling the information or using the threat of publication as their leverage. During their addressal to the FBI, the group expressed their frustration and feelings of being offended for the characterization that the agency has made regarding the group while also demanding that certain claims be taken back, but the group hasn’t since provided a clear intimation of their plan of action in a situation where these demands were ignored or left unmet.
Timeline of Events
|
Date |
Development |
|
Prior weeks |
ShinyHunters reportedly gains access to FBIJobs.gov systems (claim, unconfirmed) |
|
This week |
Message from ShinyHunters circulates online, addressed to FBI leadership |
|
Wednesday |
FBI issues public statement confirming it is investigating the claim |
|
Wednesday |
FBIJobs.gov taken offline while the review continues |
|
Ongoing |
FBI works with third-party vendors supporting the site to assess scope |
Why This Breach Is Different
Federal Agencies often find themselves being targeted by hackers and hacking groups from around the world, and for the majority, they also manage to contain the situation or only suffer from information that was already public in some form. However this particular breach has garnered critical attention from around the world, purely on the basis of the scale and the stakes involved in the database. Instead of having obtained a portion or part of the database, ShinyHunters have claimed to obtain data covering the entire active agent workforce along with the data of job applicants, an alarming set of data that could result in massive danger on its operations while also posing one the most significant personnel-data exposure challenges that we have seen over the past decade.
The FBI's History as a Hacking Target
The claim by ShinyHunters isn’t the first time for either of the parties involved, and its likely that it would not be the last either. Earlier this year, the FBI had also disclosed that it was aggressively monitoring suspicious activity on an internal system tied to sensitive surveillance and investigative work. Soon after, a pro-Iranian hacking group had claimed that it had breached an account that belonged to FBI Director Patel, while posting the director's old photographs, resume and personal documents that were not exactly government information, but quality historical material tied to the director. The frequency of such attacks is a testament to the fact that the FBI has become and remains an attractive target while also making the agency indirectly bound to responding, investigating and safeguarding itself from such claims quickly and publicly!
What This Means for Applicants and Employees
While the FBI continues its investigations, for anyone affiliated to the FBI or those who had applied in the past, the danger of an identity leak is real but as things stand, it's important to be patient with the uncertainty instead of panicking. Until any confirmation about the breach being genuine, and the exact magnitude of the leak or the confirmed list of those who were affected or the precise data that was leaked is made clear, there truly is not much that can be done at the individual level. With that being said, it’s always a wise decision, especially for those associated with the federal jobs portal to remain vigilant over their financial accounts while practising caution towards unknown calls, messages or links, even if they were claiming to be from the federal agency or any government entity in themselves.
Conclusion
It’s still an early stage to assess whether the claims made by ShinyHunters hold any value and an actual breach has occurred or whether it’s simply an attempt to threaten the agency and cause disruption, but when the claim is of such magnitude and involves threat to personnel identity, its crucial to obtain a swift and serious response after through investigations. And that’s exactly where the matter rests at now, a site that has been pulled while investigators inside the bureau test for suspicious activity and leaks while a hacker group sits upon strong claims with stern demands that they desire are met quickly. The larger public around the world watches on, hoping for a clearer picture that could change the image of the most-trusted agency for the years to come while all eyes remain set on how the story unfolds as more details are brought to light.
Latest Posts